

[Jan 02, 2022] Valid GCCC Test Answers & GIAC GCCC Exam PDF
Realistic GCCC Exam Dumps with Accurate & Updated Questions
GIAC GCCC Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
| Topic 11 |
|
NEW QUESTION 50
What is the first step suggested before implementing any single CIS Control?
- A. Develop an effectiveness test
- B. Develop a roll-out schedule
- C. Perform a gap analysis
- D. Perform a vulnerability scan
Answer: C
NEW QUESTION 51
Which projects enumerates or maps security issues to CVE?
- A. ISO 2700
- B. SCAP
- C. NIST
- D. CIS Controls
Answer: B
NEW QUESTION 52
What could a security team use the command line tool Nmap for when implementing the Inventory and Control of Hardware Assets Control?
- A. Actively identify new servers
- B. Control which devices can connect to the network
- C. Inventory offline databases
- D. Passively identify new devices
Answer: A
NEW QUESTION 53
Based on the data shown below.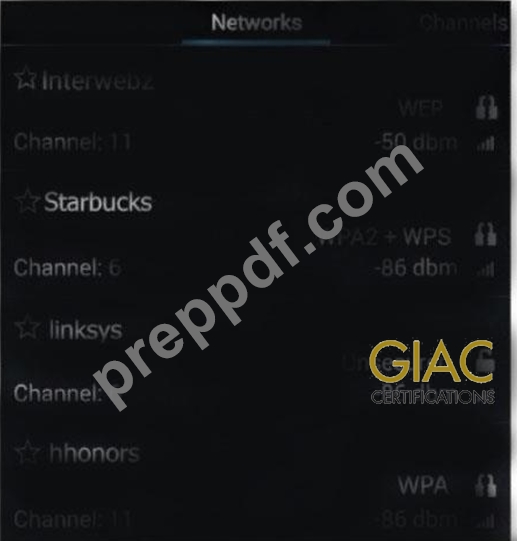
Which wireless access point has the manufacturer default settings still in place?
- A. Linksys
- B. Hhonors
- C. Starbucks
- D. Interwebz
Answer: A
NEW QUESTION 54
What is a recommended defense for the CIS Control for Application Software Security?
- A. Run a dedicated vulnerability scanner against backend databases
- B. Display system error messages for only non-kernel related events
- C. Limit access to the web application production environment to just the developers
- D. Keep debugging code in production web applications for quick troubleshooting
Answer: A
NEW QUESTION 55
Which of the following should be used to test antivirus software?
- A. FIPS 140-2
- B. Code Red
- C. EICAR
- D. Heartbleed
Answer: C
NEW QUESTION 56
Of the options shown below, what is the first step in protecting network devices?
- A. Scanning the devices for known vulnerabilities
- B. Implementing IDS to detect attacks
- C. Applying all known security patches
- D. Creating standard secure configurations for all devices
Answer: D
NEW QUESTION 57
Acme Corporation performed an investigation of its centralized logging capabilities. It found that the central server is missing several types of logs from three servers in Acme's inventory. Given these findings, what is the most appropriate next step?
- A. Restart or reinstall the logging service on each of the problem servers
- B. Perform analysis to identify the source of the logging problems
- C. Define processes to manually review logs for the problem servers
- D. Document the missing logs in the core evaluation report as a minor issue
Answer: B
NEW QUESTION 58
An organization wants to test its procedure for data recovery. Which of the following will be most effective?
- A. Verifying there are no errors in the backup server logs
- B. Verifying that backup process is running when it should
- C. Verifying a file can be recovered from backup media
- D. Verifying that network backups can't be read in transit
Answer: C
NEW QUESTION 59
How does an organization's hardware inventory support the control for secure configurations?
- A. It provides a list of managed devices that should be secured
- B. It provides a list of unauthorized devices on the network
- C. It provides the MAC addresses for insecure network adapters
- D. It identifies the life cycle of manufacturer support for hardware devices
Answer: A
NEW QUESTION 60
Which of the following assigns a number indicating the severity of a discovered software vulnerability?
- A. CVE
- B. CCE
- C. CPE
- D. CVSS
Answer: D
NEW QUESTION 61
Which of the following will decrease the likelihood of eavesdropping on a wireless network?
- A. Using EAP/TLS authentication and WPA2 with AES encryption
- B. Putting the wireless network on a separate VLAN
- C. Broadcasting in the 5Ghz frequency
- D. Using Wired Equivalent Protocol (WEP)
Answer: A
NEW QUESTION 62
Which of the options below will do the most to reduce an organization's attack surface on the internet?
- A. Ensure that rotation of duties is used with employees in order to compartmentalize the most important tasks
- B. Deploy antivirus software on internet-facing hosts, and ensure that the signatures are updated regularly
- C. Deploy an access control list on the perimeter router and limit inbound ICMP messages to echo requests only
- D. Ensure only necessary services are running on Internet-facing hosts, and that they are hardened according to best practices
Answer: D
NEW QUESTION 63
What is an organization's goal in deploying a policy to encrypt all mobile devices?
- A. Applying the principle of defense in depth to their mobile devices
- B. Enabling best practices for the protection of their software licenses
- C. Providing their employees, a secure method of connecting to the corporate network
- D. Controlling unauthorized access to sensitive information
Answer: D
NEW QUESTION 64
What tool creates visual network topology output and results that can be analyzed by Ndiff to determine if a service or network asset has changed?
- A. Zenmap
- B. Netscreen
- C. Ngrep
- D. CIS-CAT
Answer: A
NEW QUESTION 65
An organization has implemented a control for Controlled Use of Administrative Privilege. The control requires users to enter a password from their own user account before being allowed elevated privileges, and that no client applications (e.g. web browsers, e-mail clients) can be run with elevated privileges. Which of the following actions will validate this control is implemented properly?
- A. Force the root account to only be accessible from the system console.
- B. Check the log entries to match privilege use with access from authorized users.
- C. Run a script at intervals to identify processes running with administrative privilege.
Answer: C
NEW QUESTION 66
Which of the following archiving methods would maximize log integrity?
- A. Magnetic Tape
- B. CD-RW
- C. USB flash drive
- D. DVD-R
Answer: D
NEW QUESTION 67
An attacker is able to successfully access a web application as root using ' or 1 = 1 . as the password. The successful access indicates a failure of what process?
- A. Input Validation
- B. URL Encoding
- C. Account Management
- D. Output Sanitization
Answer: A
NEW QUESTION 68
How often should the security awareness program be communicated to employees?
- A. Monthly
- B. At orientation and review times
- C. Continuously
- D. Annually
Answer: C
NEW QUESTION 69
An organization has implemented a control for penetration testing and red team exercises conducted on their network. They have compiled metrics showing the success of the penetration testing (Penetration Tests), as well as the number of actual adversary attacks they have sustained (External Attacks). Assess the metrics below and determine the appropriate interpretation with respect to this control.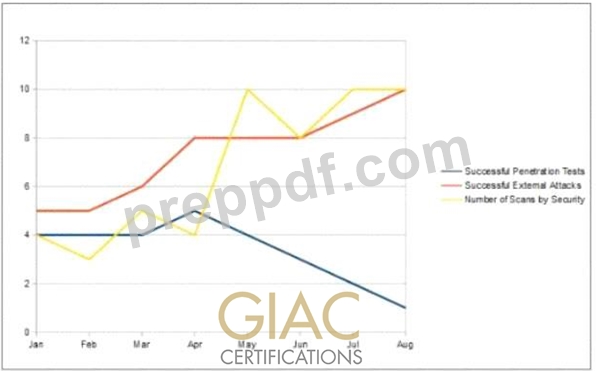
- A. The blue team is adequately protecting the network
- B. The red team is improving their capability to measure network security
- C. The methods the red team is using are not effectively testing the network
- D. There are too many internal penetration tests being conducted
Answer: C
NEW QUESTION 70
An organization has implemented a policy to detect and remove malicious software from its network. Which of the following actions is focused on correcting rather than preventing attack?
- A. Using Network access control to disable communication by hosts with viruses
- B. Disabling autorun features on all workstations on the network
- C. Training users to recognize potential phishing attempts
- D. Configuring a firewall to only allow communication to whitelisted hosts and ports
Answer: A
NEW QUESTION 71
......
GCCC Exam Dumps - PDF Questions and Testing Engine: https://www.preppdf.com/GIAC/GCCC-prepaway-exam-dumps.html
GCCC Dumps - The Sure Way To Pass Exam: https://drive.google.com/open?id=1PxqTyfKm8lhPwH6YGHEzzyOl5XGkTPAv